Reverse Engineering
4 posts filed under category “Reverse Engineering”.
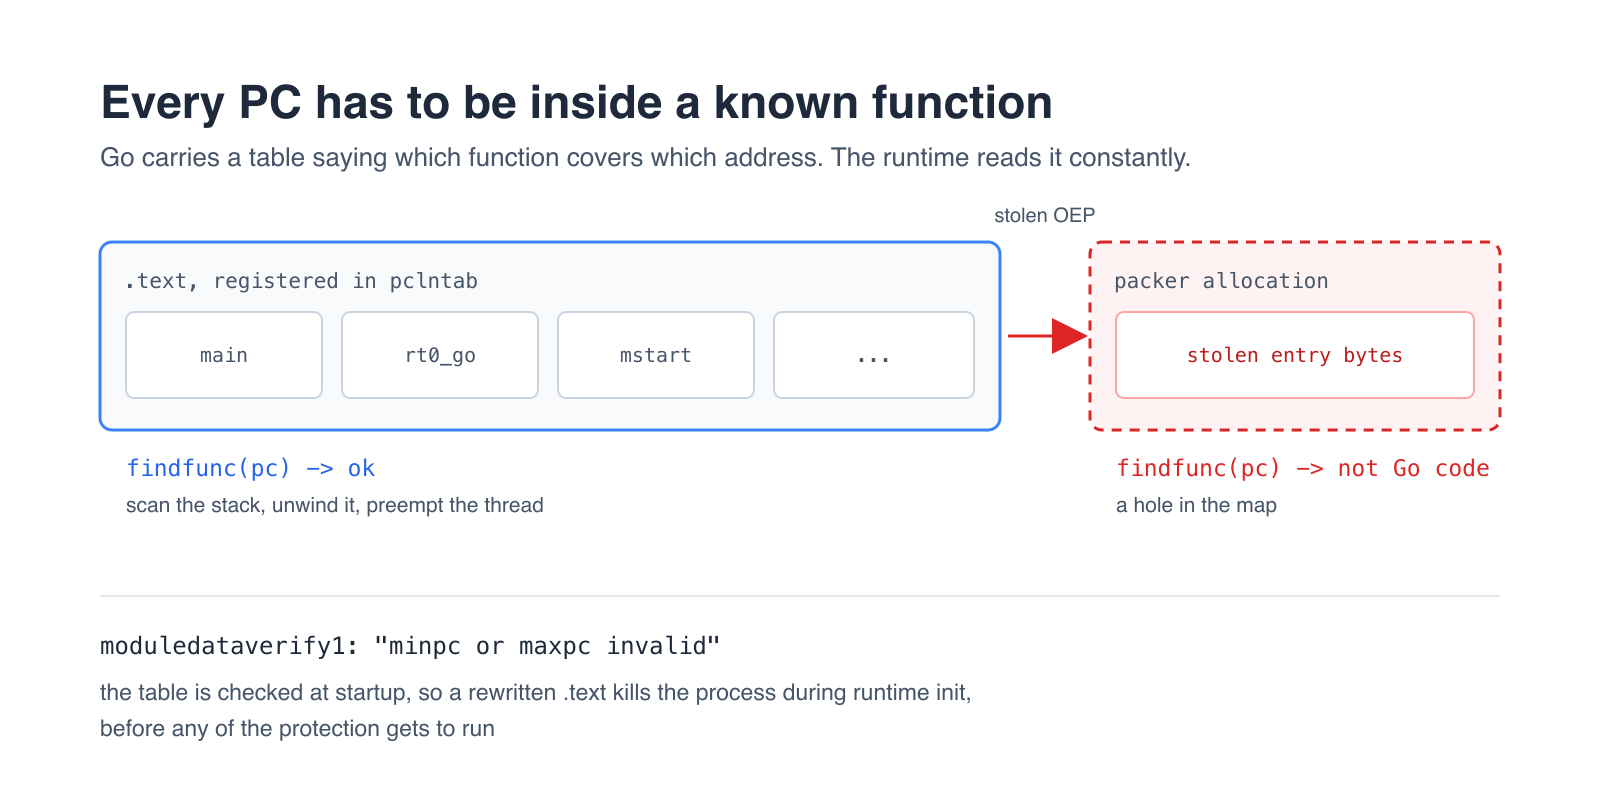
Why Go binaries need a different protector
A C binary and a Go binary are both native machine code, so the same packer should work on both. It does not. Measured differences, and what each...
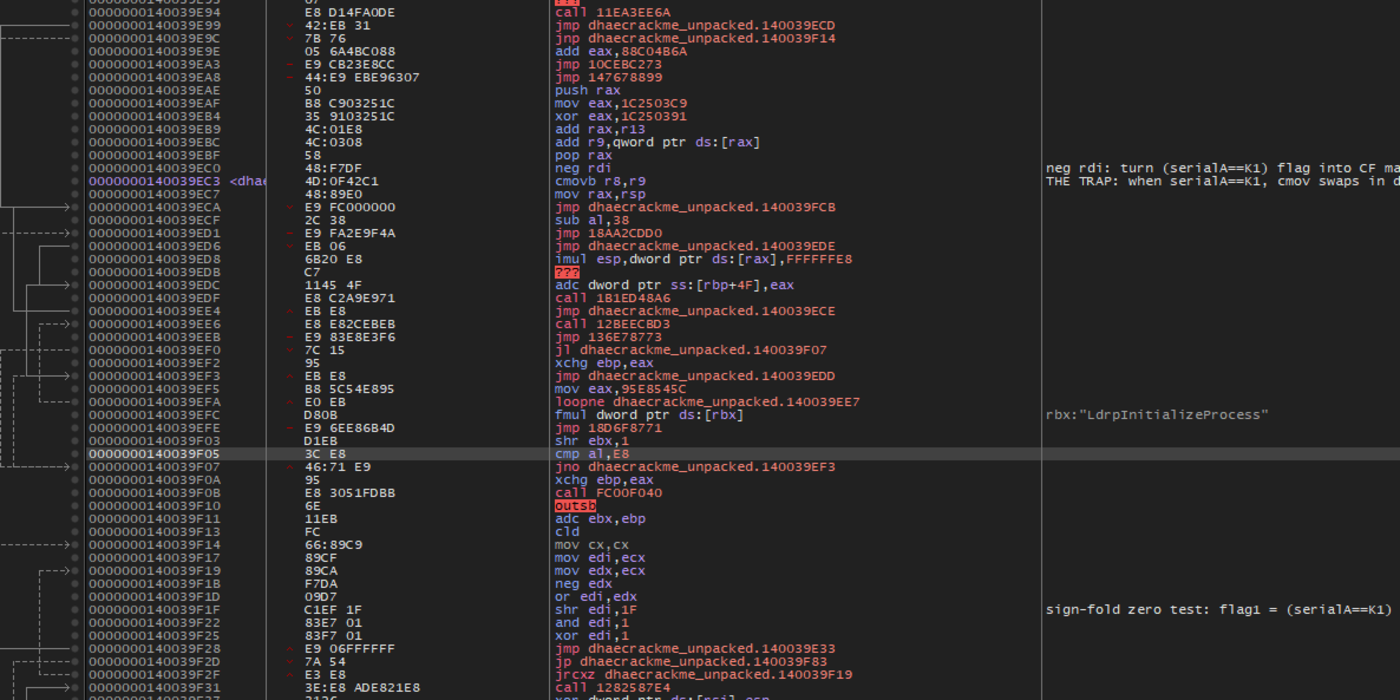
Defeating code virtualization: a keygen for a VM-protected crackme
Inside the virtual machine: an anti-single-step trap, a decoy that corrupts the value you are watching but only when your serial is right, and the fifteen lines of...
Unpacking a self-defending Windows crackme
Every section empty on disk, a three layer packer, hash-resolved imports, and a background thread that kills the process 200 ms after you patch the branch. Part one...
Introduction to software reverse engineering
Reverse engineering, in computer programming, is a technique used to analyze software in order to identify and understand the parts it is composed of. The usual reasons for...